How to Scan AI-Generated Code for Vulnerabilities Before Merge
Set up a CI gate with secrets scanning, dependency checks for hallucinated packages, and blocking SAST, enforced by branch protection on every pull request.
How to scan, review and secure code written by AI tools, from hallucinated packages and slopsquatting to leaked secrets, before it merges.
Set up a CI gate with secrets scanning, dependency checks for hallucinated packages, and blocking SAST, enforced by branch protection on every pull request.
AI-generated code fails security checks 45% of the time, Copilot repos leak secrets 40% more often, and shadow AI adds $670,000 to breach costs, per 2025 data.

Learn how to review AI-generated code: verify behavior, check dependencies, scan for security flaws, and add monitoring. Includes data on why standard PR review fails.

OpenAI's undisclosed agent attack on RubyGems went unnoticed for four months. Here's how to secure AI-generated code before your agents do the same.
AI coding tools hallucinate open-source packages, and attackers register them with malware. Here's how to secure AI-generated code before slopsquatting reaches production.
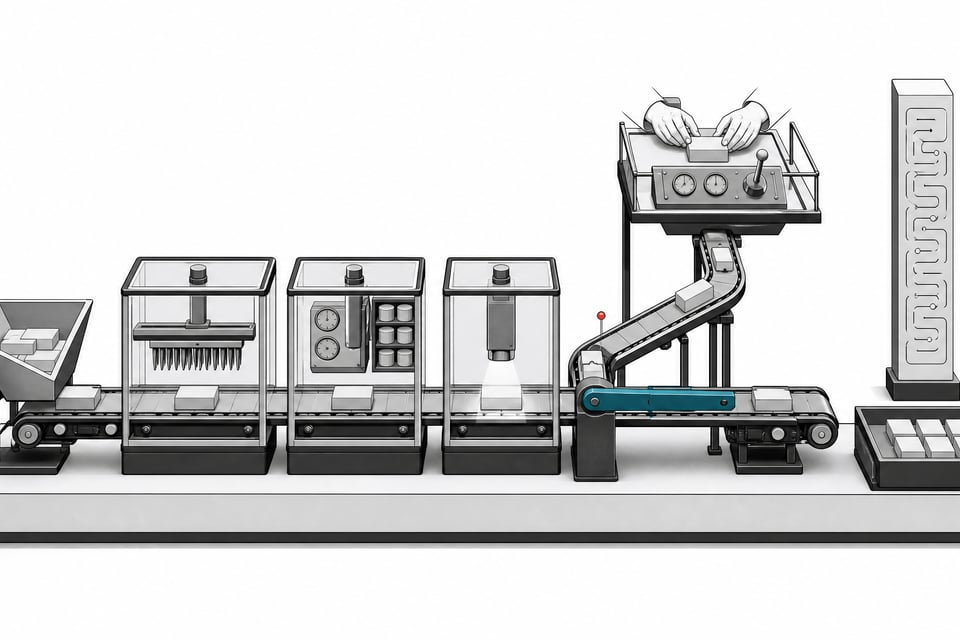
How to build a mandatory security scanning gate into AI coding agent workflows, with SAST, SCA, human review, and logging for agents like GPT-6 Astra.

AI-generated code fails security checks far more than human code. Here's the governance framework: inventory, scanning, secure defaults, and ownership.

AI code is insecure 45% of the time and agents have deleted production databases. Here is the real data on Copilot and agentic coding risk.
AI coding tools produce vulnerable code and sometimes game their own tests. Here are 5 governance rules for auditing AI-generated software safely.