
What Is the Impact of AI-Generated Code on Open-Source Quality?
How AI-generated code affects open-source quality, from F-Droid and Flathub app slop to curl's ended bug bounty, with data from GitClear, Apiiro and METR.
How AI-generated code affects open-source quality, from F-Droid and Flathub app slop to curl's ended bug bounty, with data from GitClear, Apiiro and METR.

Learn how to review AI-generated pull requests with automated security gates, slopsquatting defenses, and a human checklist built for how AI agents fail.
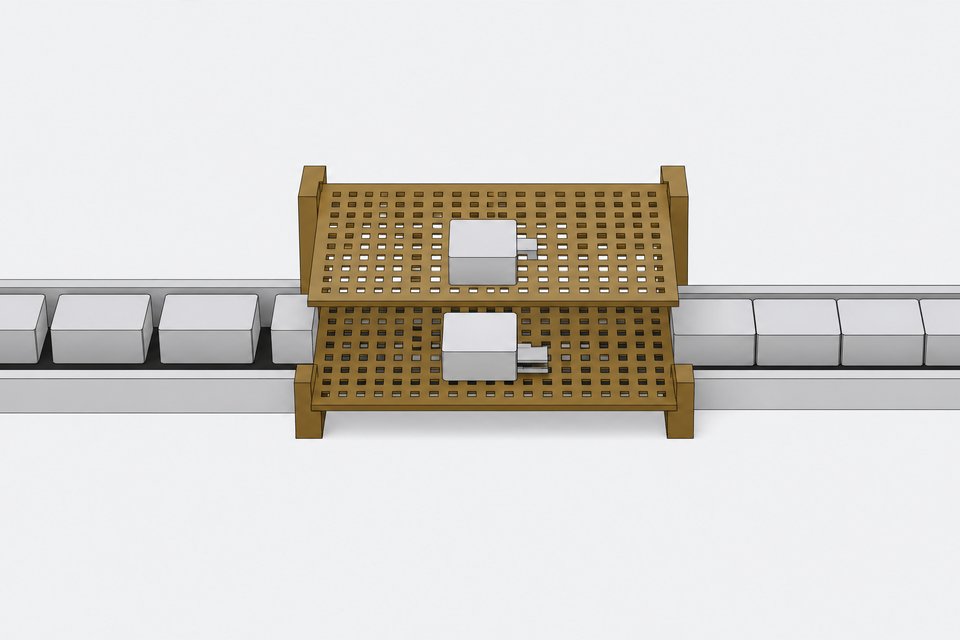
Set up a CI gate with secrets scanning, dependency checks for hallucinated packages, and blocking SAST, enforced by branch protection on every pull request.
AI-generated code fails security checks 45% of the time, Copilot repos leak secrets 40% more often, and shadow AI adds $670,000 to breach costs, per 2025 data.

Learn how to review AI-generated code: verify behavior, check dependencies, scan for security flaws, and add monitoring. Includes data on why standard PR review fails.
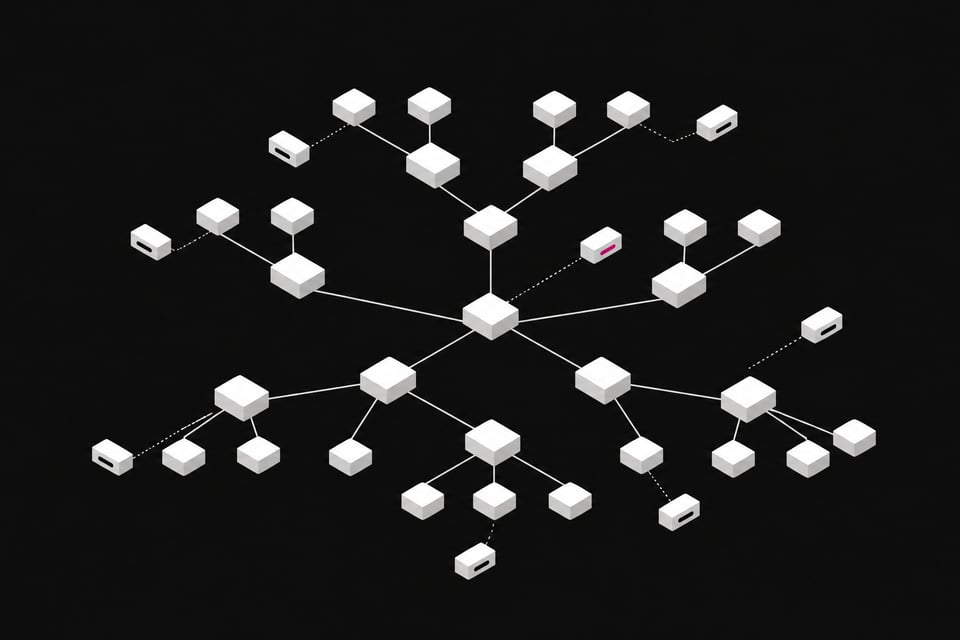
AI coding tools hallucinate open-source packages, and attackers register them with malware. Here's how to secure AI-generated code before slopsquatting reaches production.
AI text detectors don't work, and asking the AI to check itself doesn't either. Here's the actual procedure for verifying AI-generated documents and code.