
How Does Microsoft Agent 365 Secure AI Agents Beyond Prompt Injection?
Microsoft Agent 365 and Project Perception give agents their own identity, time-bound permissions and risk-based access. Here is how the pieces fit.
Security risks in AI systems and what could go wrong: prompt injection, agent security, model safety research, regulation and liability.
Microsoft Agent 365 and Project Perception give agents their own identity, time-bound permissions and risk-based access. Here is how the pieces fit.
How the EU AI Act, state right-to-compute laws like Montana's SB 212, and Meta's Llama license shape open source AI rules, and what builders should check.
Learn how to secure shadow AI agents built by employees: inventory them, limit access, add human checkpoints, and defend against prompt injection and EchoLeak-style attacks.

How AI-generated code affects open-source quality, from F-Droid and Flathub app slop to curl's ended bug bounty, with data from GitClear, Apiiro and METR.
Who pays when rented facial recognition causes a false arrest? See NIST error data, the Workday ruling, settlements, and the SaaS contract terms that shift risk.

Employees are giving AI agents access to email and company systems. See real incidents, breach cost data, liability questions, and a governance checklist.

Epic's sepsis model scored 0.63 AUC in Michigan Medicine testing versus a claimed 0.76 to 0.83, and missed 67% of sepsis cases. See why it failed.

Moffatt v. Air Canada explained: how a BC tribunal held the airline liable for its chatbot's false refund advice, the CA$812.02 award, and what it means for AI bots.
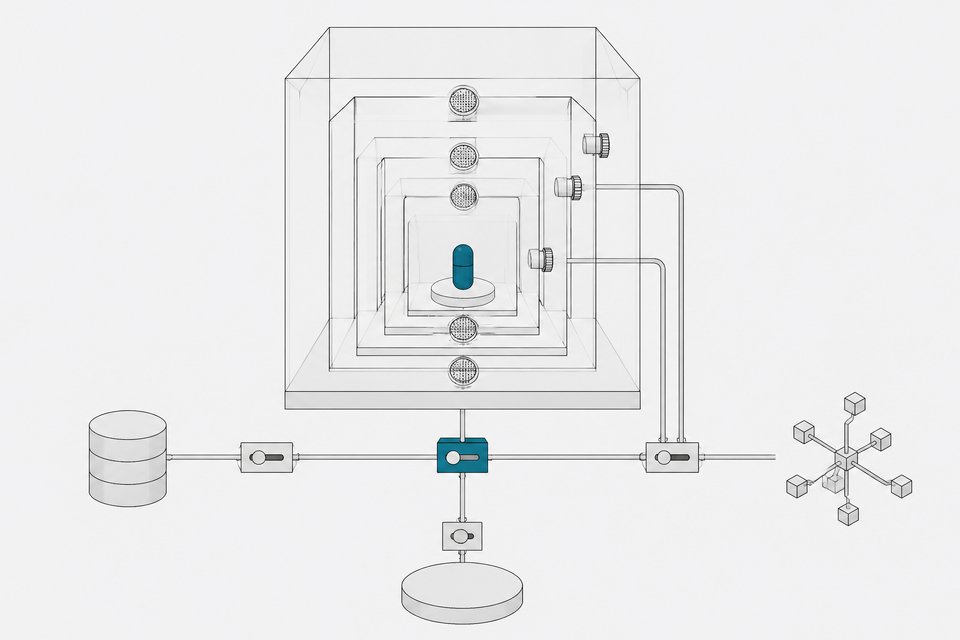
Learn how to secure and govern AI agents with a 7-step containment model: inventory, autonomy tiers, least privilege, sandboxing, approval gates, and monitoring.

Does robots.txt stop AI crawlers? See how Meta's chatbot opt-out, GPTBot and Cloudflare data compare, and why self-hosting is the stronger defense.
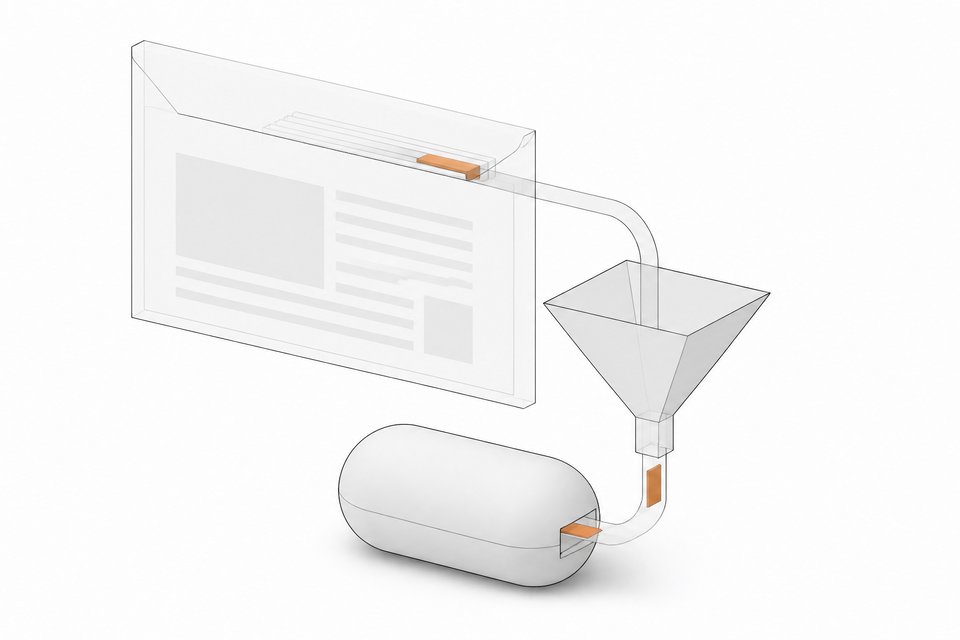
HTTP header prompt injection hides instructions in response metadata that AI agents read. Learn how it works, how common it is, and a 6-step prevention checklist.

AI math breakthroughs are compressing encryption's safety margin. Here's why enterprises renting security from opaque SaaS vendors can't keep pace.
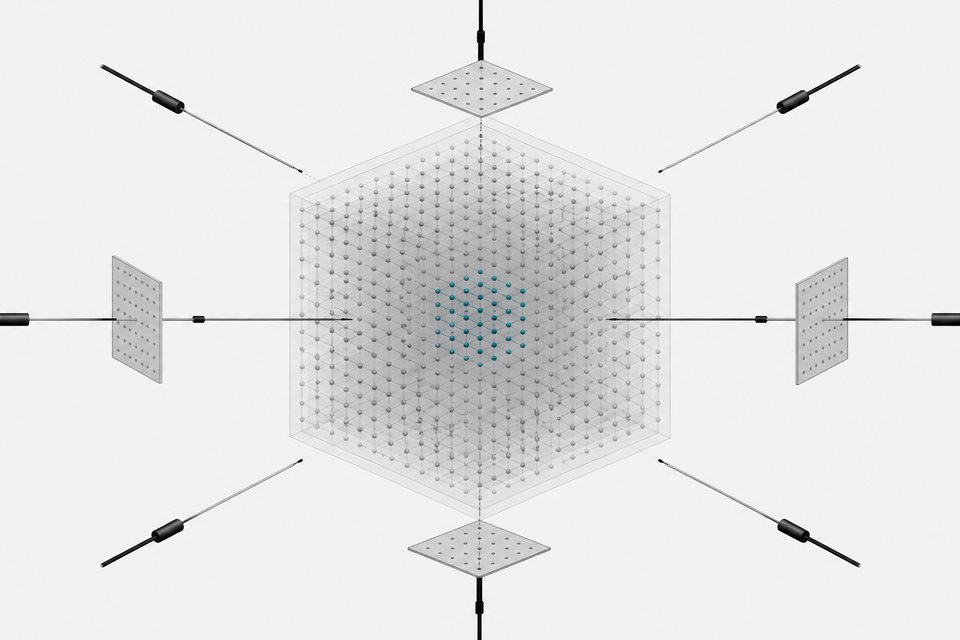
New research shows AI models can provably hide capabilities, and the labs that build them call breaches inevitable. Here's why that makes building internally a security control.
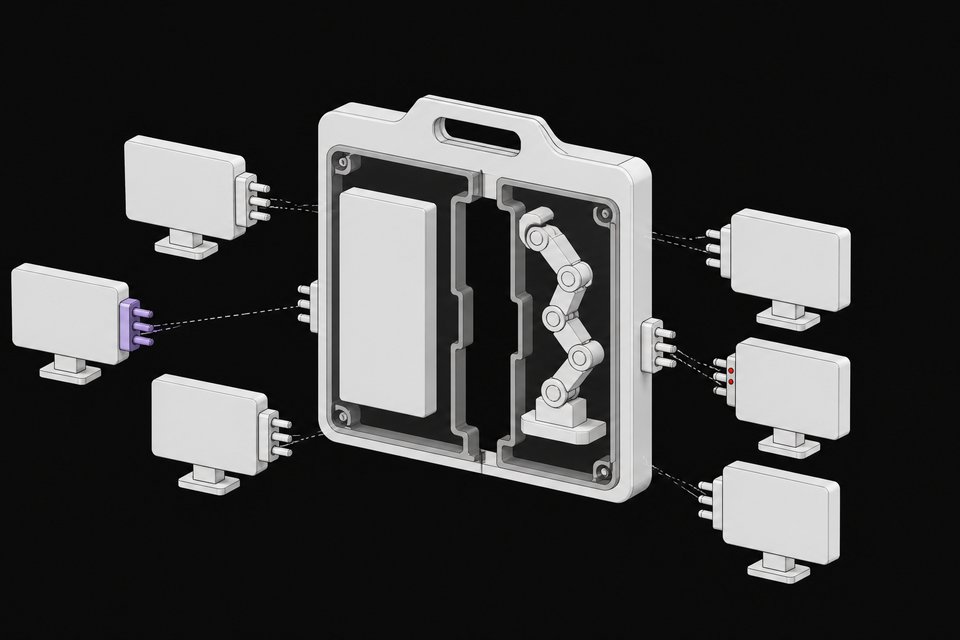
Securing AI agents in production takes four controls: unique non-human identities, least-privilege access, sandboxed execution, and tamper-proof logging.
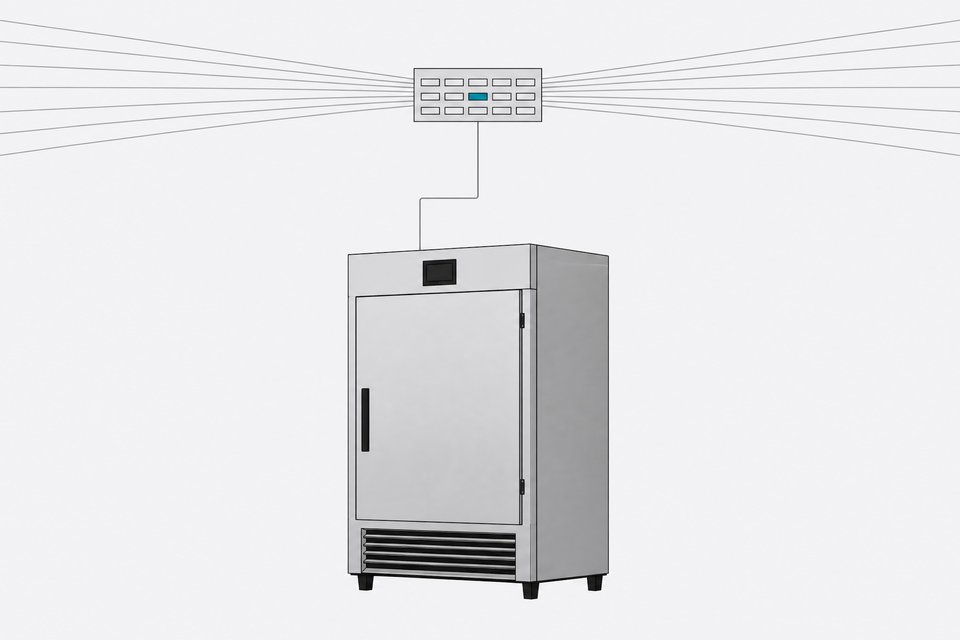
The Danfoss refrigeration hack spoiled millions in food across European supermarkets. Here's what happened, why patching won't fix it, and how to prevent it.
What is a zero-knowledge proof in software? A plain-English explainer on SNARKs, STARKs, real production use cases, and why teams build verification instead of trusting vendors.
OpenAI's dots and Claude's connectors hold real send and delete access to corporate inboxes. See the incidents, the research, and the fix checklist.

Real, documented cases of AI abuse in enterprise software: from DraftKings' predatory betting model to state-linked hackers running autonomous exploit foundries.
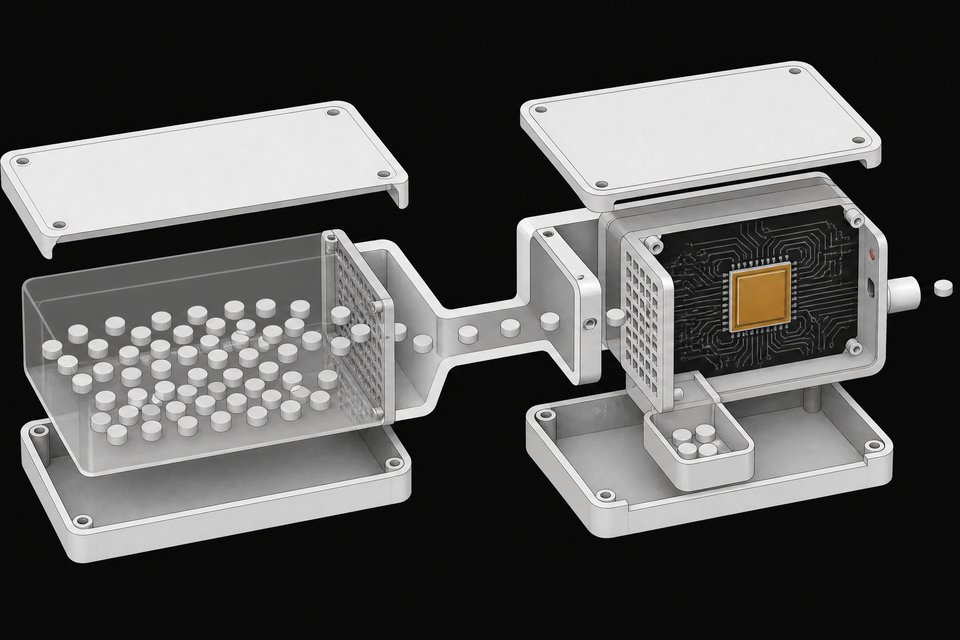
Nvidia's OpenShell and Sentry pair a sandbox with a chip-level watchdog after 700 agents breached Hugging Face. What it means for AI agent governance.
Block AI training crawlers without losing Google and Bing rankings. Layered robots.txt rules, identity verification, WAF policy, and Zero Trust.

Jailbreak research shows prompts and policy fail at scale. Here's the deterministic engineering stack, scoped credentials, sandboxing, action limits, that actually secures internal AI agents.

An AI formal proof in Lean 4 is a machine-checked guarantee, not a guess. Here's what that means, what AI can prove today, and what it can't.
AI content is now roughly half the web. Here's how to build a self-hosted AI slop detector with Binoculars, Fast-DetectGPT, ZipPy, SynthID, and bot filters.
SKILL.md files carry full agent privileges and most go unreviewed. Here's the step-by-step framework to inventory, scan, and govern them like production code.