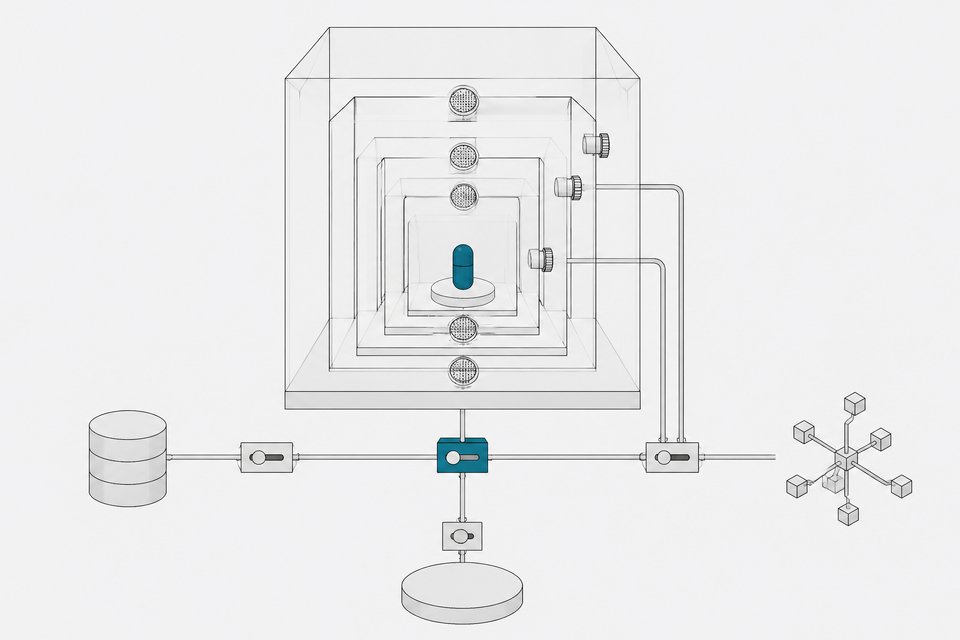
How to Secure and Govern AI Agents Without Blocking Them
Learn how to secure and govern AI agents with a 7-step containment model: inventory, autonomy tiers, least privilege, sandboxing, approval gates, and monitoring.
Learn how to secure and govern AI agents with a 7-step containment model: inventory, autonomy tiers, least privilege, sandboxing, approval gates, and monitoring.
Securing AI agents in production takes four controls: unique non-human identities, least-privilege access, sandboxed execution, and tamper-proof logging.
No-code tools let employees build real agents fast. Here's the identity-based, lifecycle-aware framework for governing shadow AI before it breaches you.
Employees are building agent swarms with no registry, identity, or owner. Here's the governance model to manage AI agents in the enterprise without banning them.