PHP Critical Vulnerabilities: What Happened and Who Is at Risk?
Two critical PHP flaws, found with AI help, led the NSA and Japan to urge patching or taking sites offline. Here is what happened and who is exposed.

What are the critical PHP vulnerabilities?
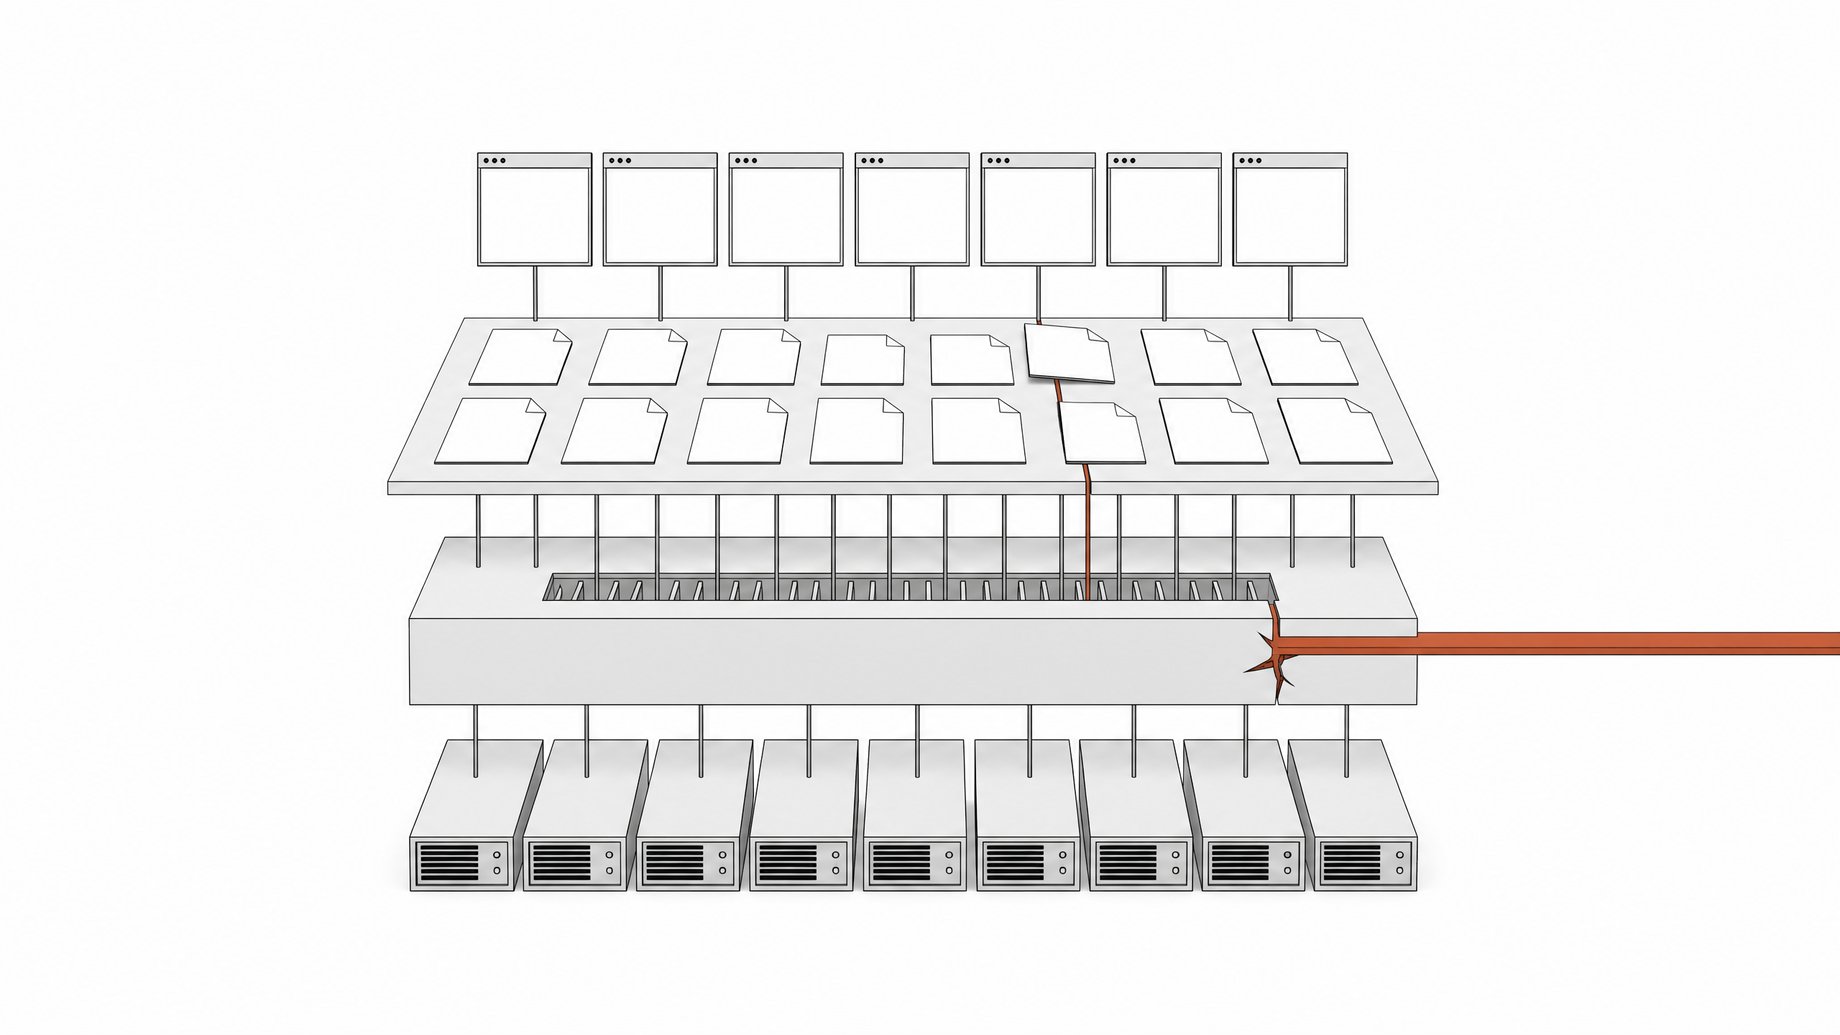
Two critical flaws in PHP, the server-side language behind an estimated 70% of websites, prompted urgent warnings from the NSA's cybersecurity account and the Japanese government. The NSA said these bugs often give a direct path to a server's file system or database. Researchers working with AI models chained one of them into remote code execution against WordPress. Officials advised patching immediately, or taking systems offline if patching is not possible.
This is a fast-moving story. The material behind this article comes from early coverage, and some details were still unconfirmed at the time. Check PHP's official security announcements for exact versions and fixes.
TL;DR
- Two critical PHP flaws drew a public warning from the NSA, which said organizations should prepare for an update immediately.
- The NSA's guidance is blunt: if you cannot update right away, take the system offline until it is fully mitigated.
- Japan's government made a similar request, saying that suspending websites can reduce risk when patching is difficult.
- Under the right conditions, an attacker may be able to run code without logging in, which is why WordPress sites are a focus of concern.
- Unmaintained sites are the most exposed, because nobody is around to apply the patch.
- The flaws were found with help from AI models during OpenAI's Patch the Planet effort, and the security firm Calif published a detailed write-up.
What exactly did the NSA and Japan say?
The NSA cyber account said that, effective immediately, all organizations using PHP should be prepared for an update addressing two critical vulnerabilities. It noted that PHP is widely used for web applications and that these kinds of flaws often provide a direct path to the server's file system or database. If an immediate update is not feasible, it recommended taking the system offline until it can be fully mitigated.
Japan's Prime Minister issued an urgent public request to act that night. She said the PHP security team had warned about two critical vulnerabilities, and that where applying the fixed patch promptly is difficult, suspending websites and similar measures can be an effective way to reduce risk. Commentators summarized this as: if you run a PHP site and have not patched, consider shutting it down.
Coverage also claimed that parts of the Dutch government shut down services and that some EU governments took sites offline. One creator hedged that claim as slightly exaggerated. Treat those reports as unconfirmed unless you see an official statement.
Why does remote code execution on WordPress matter?
Remote code execution (RCE) means an attacker runs their own commands on your server. Normally, doing meaningful things on a WordPress site requires logging in. The concern here is that, under the right conditions, an attacker could execute code without authenticating.
WordPress matters because it is built on PHP and powers a huge share of content sites. A compromised server can expose files and databases, and it can also be turned against visitors. One creator pointed out that a familiar, trusted site could be altered to harvest visitor information, so a site you recognize is no guarantee of safety during the patch window.
How were the PHP flaws found?
The research came out of Calif, a cybersecurity company, working under OpenAI's Patch the Planet initiative. That program aims to fix critical bugs before attackers find them. According to the coverage, the team used OpenAI models and some Gemini models.
The target was how PHP behaves when it is interrupted, particularly around out-of-memory conditions. When PHP runs out of memory, it has to clean up, and that cleanup path is where the weakness sits. Calif described finding the first out-of-memory fatal error and the first of three interruption points, which together let them piece together an RCE against WordPress.
One researcher then asked the model to generalize what they had done into a reusable skill file, a set of instructions for hunting similar bugs. Each new finding could improve the skill, and the model could explore many paths in parallel. That loop is a large part of why people see this as a preview of AI-accelerated vulnerability research. OpenAI reportedly called the bug one of the most impactful vulnerabilities in recent memory, though I could not verify that wording independently.
Who is most at risk?
The consistent answer across the coverage is sites that nobody maintains. A public advisory only helps if someone reads it and applies the fix.
| Group | Why it is exposed | What to do |
|---|---|---|
| Abandoned or unmaintained PHP sites | No one is watching for updates | Patch, or take the site offline |
| Small and mid-sized organizations | Fewer security staff, slower patching | Prioritize the update and confirm it is live |
| WordPress site owners | Large, widely targeted PHP platform | Update PHP and keep core, themes, and plugins current |
| Visitors to unpatched sites | A trusted domain may serve malicious content | Be cautious, use MFA, watch for suspicious prompts |
One analysis argued that large, well-resourced companies, and organizations with early access to AI security programs like Anthropic's Project Glasswing or OpenAI's equivalent, are better positioned than smaller operators outside that circle. That is an opinion rather than a measured result, but it matches the basic logic of patch speed.
There were also unverified signs of active exploitation. One creator said Cloudflare was already seeing early attacks, and that the technical details may have leaked online before the patch. He said he could not confirm either claim, so weigh them accordingly.
What should site owners do right now?
- Find out what you run. Identify every PHP application you host, including old marketing sites and forgotten staging servers.
- Apply the official PHP update as soon as your distribution or host ships it. Then confirm the fix is actually running, not just downloaded.
- Update WordPress core, themes, and plugins alongside PHP.
- Take unpatchable systems offline until you can mitigate them, as the NSA advised.
- Cut your attack surface. Retire sites you do not need, and question whether each one needs logins, APIs, or stored customer records.
- Consider delegating sign-in to a large identity provider through OAuth instead of storing passwords yourself.
What should everyday users do?
You cannot patch someone else's server, so the goal is to limit damage.
- Use an authenticator app or a hardware security key instead of SMS codes. One creator said most phone number services have proven pretty trivially easy to break into.
- Use a unique password for every account, so one leak does not cascade.
- Be wary of links in texts and emails, and keep your browser, OS, and apps updated.
- Delete accounts you no longer use, especially ones that hold repeated personal details.
- Change passwords on sites where a breach would hurt, since data entered earlier could already be exposed.
One creator also suggested agreeing on a verification phrase with family members, to defend against AI-assisted impersonation scams.
Is this part of a bigger trend?
The coverage framed it that way. Creators cited a run of AI-linked incidents, including large data exposures at Japanese companies and a claim that hackers used Claude, Grok, and Kimmy to automate a cyberattack on 400 banks. Those figures come from the videos and I could not confirm them. A separate story about a certificate provider with weak private keys was presented as related, but it is a different issue from the PHP flaws.
The more defensible takeaway is structural. Models that can find and chain memory-handling bugs shorten the time between discovery and exploitation. That puts pressure on every team that treats patching as a quarterly chore.
Frequently Asked Questions
Do I really need to shut down my PHP site?
Only if you cannot patch promptly. The NSA and Japan both framed offline status as the fallback when an immediate update is not feasible. If you can apply the official fix quickly and verify it, you do not need to go dark.
Is every WordPress site vulnerable?
Not necessarily. The reported WordPress RCE depends on "the right conditions," and the sources do not spell those out. Assume exposure until your PHP version is updated, then check the vendor's advisory for specifics.
Who found the PHP vulnerabilities?
The security company Calif found them while participating in OpenAI's Patch the Planet initiative, using OpenAI and Gemini models. Calif published a long technical write-up. The PHP security team issued the warning about the two critical flaws.
What is the single most useful step for regular users?
Switch accounts that matter to an authenticator app or hardware key, and use unique passwords. Neither stops a server breach, but both limit what an attacker can do with stolen credentials.
Where can I get exact patch versions?
Use PHP's official release and security announcements, plus your hosting provider or Linux distribution's advisories. The videos covering this early did not give version numbers, so check primary sources rather than relying on summaries.
How we source, write, and correct our articles. Editorial standards